Access Control Installation Cost: A Realistic Budget Guide

Understanding access control installation cost begins with recognising what you're actually purchasing: not just a lock and keypad, but a networked system comprising readers, controllers, power supplies, management software, credentials, and integration with existing fire and security infrastructure. For commercial buildings in 2026, budgets typically range from £800 to £3,500 per controlled door, with the final figure determined by equipment specification, site complexity, regulatory compliance requirements, and the degree of integration needed with fire alarm systems, intruder detection systems and CCTV networks. This guide provides facility managers and responsible persons with a framework for accurate budgeting and a clear understanding of where your investment is directed.

What You're Actually Buying: The Components of Access Control Installation Cost

The access control installation cost comprises several distinct elements, each with its own price range and specification considerations. Understanding these components helps you challenge vague quotations and ensure you're comparing like with like.

Hardware at the Door

Every controlled entry point requires:

  • Card readers or biometric devices: Proximity readers (MIFARE DESFire, OSDP-compliant) cost £150–£400 each; fingerprint or facial recognition units start at £500
  • Electric locks or magnetic locks: Fail-safe maglocks (releasing on fire alarm activation per BS 7273-4) cost £200–£600; motorised locks range from £300–£900
  • Request-to-exit sensors: Infrared or microwave devices (£80–£200) detect legitimate exit and prevent false alarms
  • Door position switches: Magnetic contacts (£15–£40) monitor door status and trigger alerts for forced or held-open conditions
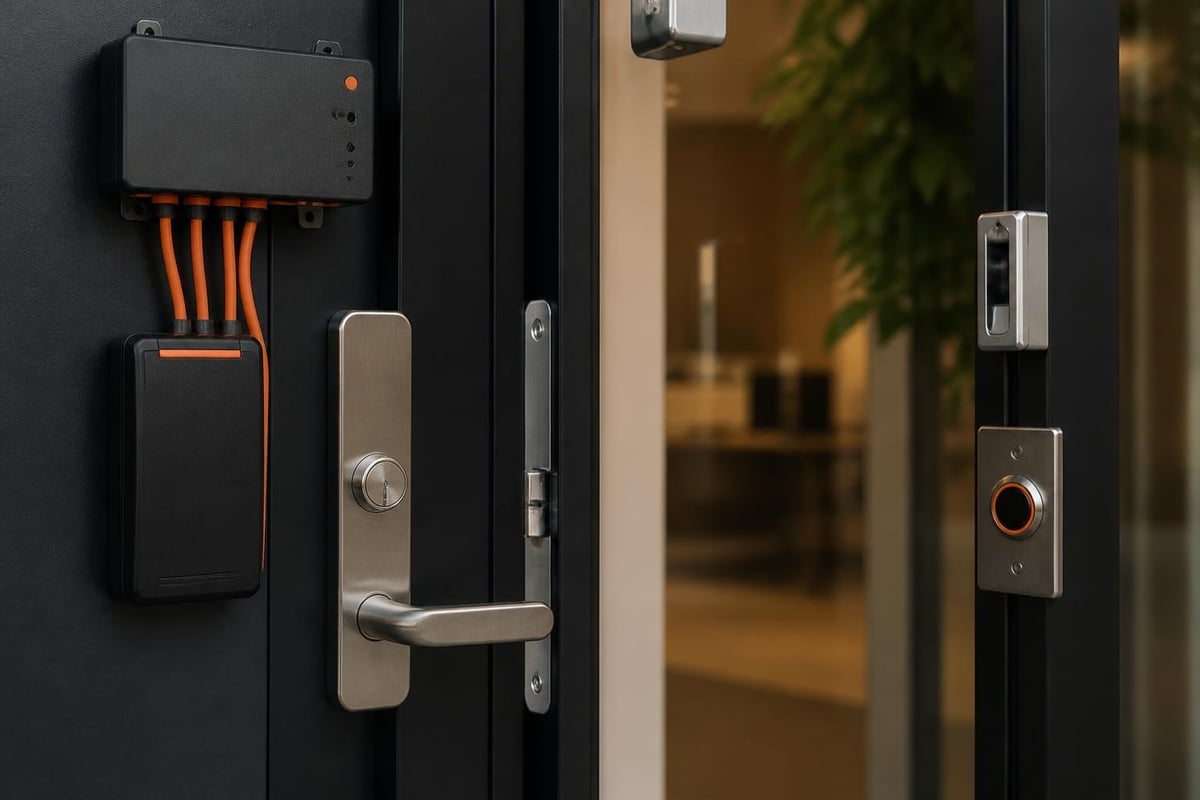
Access control door components

Controllers and Infrastructure

Door controllers are the intelligence layer that enforces access rules:

  • Single-door controllers: £180–£450 per door, typically PoE-powered for simplified cabling
  • Multi-door controllers: £600–£2,000 units managing 2–8 doors, reducing per-door cost at scale
  • Network switches and cabling: Cat6 structured cabling and PoE switches add £100–£300 per door depending on cable run length
  • Power supplies and backup batteries: Ensuring fail-safe operation during mains failure, £150–£400 per door cluster

The Physical Access Control Systems customer ordering guide published by GSA provides detailed topology descriptions showing how these components interconnect, informing realistic cost planning for multi-door installations.

Management Software and Licences

Central management software is where access control installation cost often includes hidden surprises:

  • Server software licences: £2,000–£15,000 depending on door count and feature set (visitor management, mobile credentials, API integration)
  • Per-door or per-user licences: Annual fees of £40–£150 per door are common with cloud-based platforms
  • Workstation clients: Additional licences for security desks or HR personnel managing credentials (£300–£800 per seat)
  • Integration modules: Connecting to fire, CCTV or building management systems may require add-on licences (£500–£3,000 per integration)

Cost Per Door: Realistic Pricing Bands for 2026

Access control installation cost expressed on a per-door basis provides the clearest benchmark for budgeting, though total project cost depends heavily on door count and system architecture.

System Tier Per-Door Cost Typical Components Best For
Entry-level standalone £800–£1,200 Proximity reader, electric strike, basic controller, offline operation Low-security internal doors, small sites (under 10 doors)
Networked IP system £1,400–£2,200 OSDP reader, PoE controller, network cabling, central software, credentials Standard commercial installations, most offices and warehouses
High-security integrated £2,400–£3,500 Biometric reader, certified components, fire/intruder integration, redundant servers Data centres, pharmaceutical, critical infrastructure, regulated environments

The access control market analysis published by Grand View Research in 2026 confirms these ranges align with UK commercial installations, with the mid-tier networked IP category representing approximately 65% of new projects.

Economies of Scale

Your per-door access control installation cost decreases significantly with door count:

  • 1–5 doors: £2,200–£3,500 per door (proportionally higher software and server costs)
  • 10–25 doors: £1,400–£2,000 per door (infrastructure costs spread across more endpoints)
  • 50+ doors: £1,000–£1,600 per door (volume discounts, efficient cabling runs, shared controllers)
  • 100+ doors: £850–£1,300 per door (enterprise licensing, dedicated servers justified)

These figures assume standard installation conditions; sites requiring extensive civil works, asbestos surveys, listed building consents or out-of-hours working see costs rise by 20–45%.

Wired Versus Wireless Locks: Installation Cost Trade-offs

The choice between wired and wireless access control dramatically affects installation cost, though total cost of ownership tells a more complex story.

Wired Systems

Traditional hardwired installations dominate commercial projects:

Advantages affecting cost:

  • Lower ongoing maintenance and battery replacement costs
  • Greater reliability in high-traffic applications (no radio interference or battery failures)
  • PoE delivery of power and data via single Cat6 cable reduces cabling complexity
  • Compliance with BS 7273-4 for fail-safe fire door release is straightforward
  • Integration with existing structured cabling and network infrastructure

Cost considerations:

  • Cable installation adds £150–£400 per door depending on run length and building fabric
  • Conduit and trunking for surface-mounted installations in finished buildings
  • Making-good costs for concealed cabling in plasterboard or masonry walls
  • Access equipment (scissor lifts, tower scaffolds) for high-level cable runs

Wireless and Battery-Powered Solutions

Wireless locks reduce installation labour but introduce different cost factors:

Where they reduce access control installation cost:

  • Minimal cabling saves £200–£500 per door in labour and materials
  • Faster installation (typically 2–3 hours per door versus 4–6 for wired)
  • Ideal for listed buildings, glass partitions or locations where cable runs are impractical
  • Retrofit scenarios where existing decorative finishes must be preserved

Hidden cost factors:

  • Hardware costs are 20–40% higher (battery-powered locks cost £450–£1,200 versus £200–£600 for wired)
  • Battery replacement every 2–4 years adds £40–£80 per door in parts and labour
  • Radio frequency surveys may be needed in complex buildings (£800–£2,000)
  • Limited integration options with fire alarm systems increase compliance complexity

The global access controls study by The Freedonia Group identifies wireless growth driven by retrofit demand, though total cost of ownership typically favours wired solutions over 10-year lifecycles.
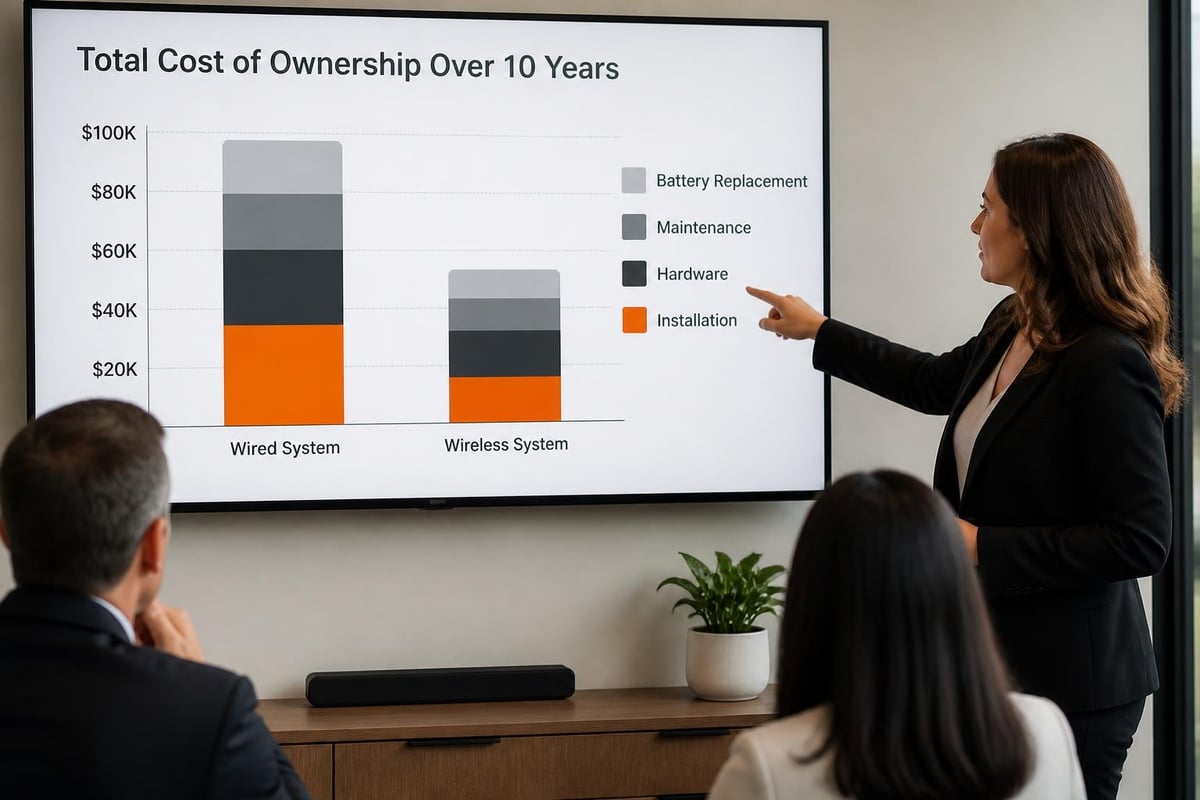
Wired versus wireless cost comparison

Integrating Fire Door Release, Intruder Detection and CCTV

The access control installation cost increases substantially when systems must integrate with existing commercial security systems, but this integration delivers critical safety and operational benefits.

Fire Alarm Integration and BS 7273-4 Compliance

The Regulatory Reform (Fire Safety) Order 2005 requires that locked final exit doors release automatically upon fire alarm activation. BS 7273-4 specifies the interface arrangements:

  • Fail-safe electromagnetic locks: Release when power is removed by fire alarm system relay outputs
  • Interface modules: Fire panel to access control system signalling (£300–£800 per zone)
  • Emergency break glass units: Manual override points adjacent to final exits (£120–£250 each)
  • Battery backup: Ensures fire alarm can trigger release during mains failure (included in controller costs above)

Integration adds £400–£900 per fire exit door to access control installation cost, but is non-negotiable for regulatory compliance. The NIST guidance on PACS provides technical detail on fail-safe versus fail-secure lock selection that informs specification decisions.

Intruder Alarm System Integration

Connecting access control to intruder detection creates intelligent security zones:

Integration scenarios and costs:

  • Basic door contacts to alarm panel: Existing access control door position switches wired into intruder zones (£150–£300 per door)
  • Two-way communication: Access system arms/disarms alarm panels based on user credentials (£600–£1,500 integration licence plus £200–£400 labour)
  • Alarm-triggered lockdown: Intrusion detection triggers automatic door locking and CCTV recording (£800–£2,000 system integration)

This integration is particularly valuable in warehouse security alarm systems and distribution centres where goods-in/goods-out areas require coordinated security responses.

CCTV and Video Management Integration

Linking access events to video footage provides audit trails and incident investigation capability:

  • Event-triggered recording: Card swipes trigger CCTV bookmarks or recording sequences (£400–£1,200 integration module)
  • Video verification at entry: Security personnel see live video when access is requested (requires additional monitors and interface licensing, £1,500–£3,500)
  • Facial recognition verification: Biometric comparison of card holder to CCTV image (£2,000–£5,000 per door for high-security applications)

The comprehensive approach to security and access control integration ensures that multiple protective layers work cohesively rather than as isolated systems.

Hidden Costs: Licences, Credentials and Maintenance

Quoted access control installation cost often excludes ongoing operational expenses that significantly affect total cost of ownership.

Software Licences and Annual Fees

  • Annual support contracts: 15–22% of software licence value per year (£300–£3,300 annually for typical 20-door systems)
  • Cloud service subscriptions: £8–£25 per door per month for hosted platforms (£96–£300 per door annually)
  • Mobile credential platforms: £3–£8 per user per month for smartphone-based access
  • Software version upgrades: Major releases may require additional licensing (£500–£2,000 every 3–5 years)

Credentials and Consumables

Every authorised person requires a physical or digital credential:

  • Proximity cards: £1.50–£4 each (MIFARE Classic); £3–£8 for secure MIFARE DESFire EV2
  • Key fobs: £2–£6 each for durable ABS enclosures
  • Printed card customisation: Photo ID printing adds £0.80–£2 per card in materials and labour
  • Card printer hardware: £800–£3,500 for direct-to-card or retransfer printers (amortised across credentials)
  • Biometric enrolment: 10–15 minutes per user at typical £45/hour labour rates

A 100-employee site issuing secure photo ID cards incurs £500–£1,200 in initial credential costs, with replacement cards for losses running at approximately 8–12% of headcount annually.

Maintenance and Callout Costs

The PACS selection guide published in peer-reviewed literature emphasises lifecycle planning:

  • Preventive maintenance visits: £180–£350 per visit (recommended quarterly for critical sites)
  • Reactive callout charges: £120–£200 for first hour, then £60–£90 per subsequent hour
  • Parts replacement: Readers, locks and controllers have 7–12 year service lives; budget 5–8% of hardware value annually
  • Database administration: 2–6 hours monthly for user management, audit reviews and credential updates

Budget Bands: What Different Price Points Deliver

Understanding how access control installation cost correlates with capability helps you specify appropriately for your risk profile and operational needs.

£800–£1,200 Per Door: Basic Standalone

What you get:

  • Individual door controllers with offline operation
  • Proximity card readers (125kHz or basic MIFARE)
  • Electric strikes or surface-mounted maglocks
  • Manual programming via controller keypad
  • No central software or reporting
  • Limited user capacity (100–500 credentials per controller)

Appropriate for:

  • Internal office doors with low security requirements
  • Server rooms or storage areas in small businesses
  • Temporary or trial installations
  • Sites with minimal audit or compliance obligations

Red flags: No audit trail, no remote management, difficult to revoke credentials urgently, poor scalability.

£1,400–£2,200 Per Door: Networked IP Standard

What you get:

  • Network-connected controllers with central management software
  • OSDP-compliant readers with secure credential authentication
  • Fail-safe locks with fire alarm integration capability
  • Real-time monitoring and event logging
  • Time-based access rules (access granted only during working hours)
  • Integration with HR systems for automated user provisioning
  • Capacity for 10,000+ users system-wide

Appropriate for:

  • Typical commercial offices, warehouses and retail back-of-house
  • Multi-tenant buildings requiring separated access rights
  • Sites requiring audit trails for insurance or client requirements
  • Businesses with 20+ employees and moderate security risk

This tier represents best value for most commercial installations and aligns with industry standard implementations.

£2,400–£3,500 Per Door: High-Security Integrated

What you get:

  • Biometric verification (fingerprint, facial recognition or iris scanning)
  • FIPS 201-compliant components certified through the FIPS 201 Evaluation Program
  • Redundant servers and failover networking
  • Anti-passback and anti-tailgating enforcement
  • Multi-factor authentication (card plus PIN plus biometric)
  • Full integration with fire, CCTV, building management and alarm monitoring systems
  • Encrypted credential data and secure communications
  • Comprehensive audit logging with tamper-evident storage

Appropriate for:

  • Data centres, research facilities and pharmaceutical manufacturing
  • Sites holding valuable assets or sensitive information
  • Regulated industries (defence, finance, healthcare)
  • Critical national infrastructure

Compliance driver: Many sectors mandate specific security standards that necessitate this investment regardless of door count.
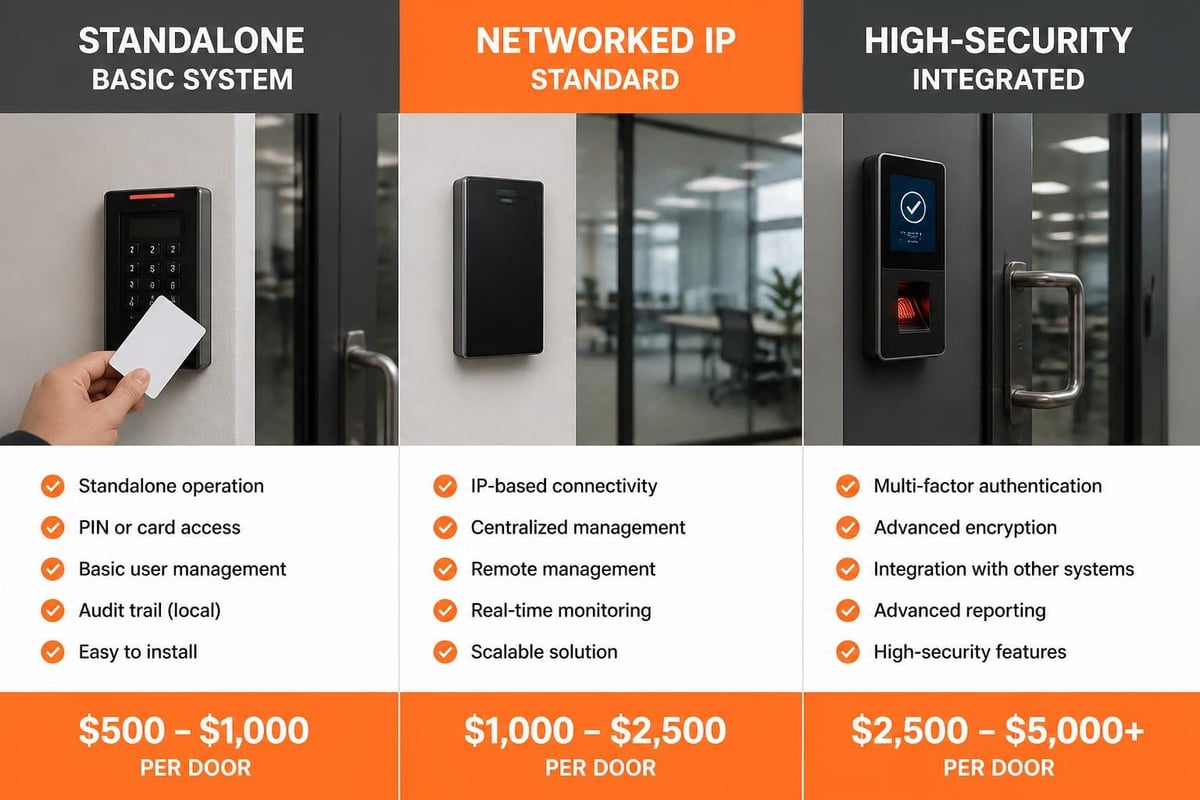
Budget tier comparison

Cheap-Quote Red Flags: When Low Prices Signal Problems

Unusually low access control installation cost quotations often hide deficiencies that compromise security, compliance or total cost of ownership.

Specification Warning Signs

Non-compliant components: Electromagnetic locks that are fail-secure (remaining locked during fire alarm activation) violate BS 7273-4 and the Regulatory Reform (Fire Safety) Order 2005. Ensure specifications explicitly state fail-safe operation for all final exit doors.

Proprietary readers: Systems using manufacturer-specific credential formats lock you into single-source purchasing. Insist on open standards (MIFARE DESFire, OSDP) that allow credential and reader portability.

Inadequate power backup: Battery backup must maintain fail-safe operation for minimum four hours. Cheap installations omit batteries or use undersized units that fail during extended power cuts.

Missing documentation: Professional installations include as-built drawings, programming documentation, and operation manuals. Absence of these documents indicates poor project management and creates long-term support difficulties.

Commercial Practice Concerns

Be cautious of:

  • Verbal-only quotations: Legitimate contractors provide detailed written specifications and breakdowns
  • Pressure to sign quickly: Professional firms allow time for tender comparison and technical review
  • No site survey: Accurate pricing requires physical assessment of cable routes, door types, network infrastructure and power availability
  • Unlicensed software: Pirated management software exposes you to legal liability and lacks vendor support
  • No ongoing support: Installation-only contracts with no maintenance provision leave you stranded after handover

The Secure Technology Alliance physical access publications provide implementation guidance that helps you evaluate whether contractors understand current standards and best practices.

Labour and Experience Factors

Access control installation requires specific competencies:

  • Network cabling certification: Cat6 data cabling should be installed by certified technicians and tested to TIA-568 standards
  • Fire alarm competence: BS 7273-4 integration must be designed and commissioned by engineers with fire alarm qualifications
  • Software configuration expertise: Complex access rules, integration logic and database management require trained specialists

Quotations significantly below market rates often reflect use of unskilled labour, leading to commissioning delays, poor reliability and safety non-compliance. The investment in experienced contractors typically repays itself within months through reduced fault callouts and faster system optimisation.

Long-term Cost Implications

The cheapest access control installation cost often becomes the most expensive over time:

Comparison over 10 years:

Factor Budget Installation Professional Installation
Initial cost (20 doors) £16,000 £28,000
Callout costs (10 years) £8,000–£15,000 £2,000–£4,000
Parts replacement £6,000–£9,000 £3,000–£5,000
System replacement (year 5–7) £18,000–£22,000 Not required
Total 10-year cost £48,000–£62,000 £33,000–£37,000

Quality installations from experienced contractors deliver lower total cost of ownership, better uptime, and simpler compliance demonstration during audits or insurance renewals.


Access control installation cost varies widely based on specification, integration requirements and site complexity, but understanding the components, budget tiers and hidden costs enables informed decision-making that balances initial expenditure against long-term value and compliance obligations. Whether you need basic door control or fully integrated security solutions, Logic Fire and Security brings decades of experience designing and installing access control systems for Blue Chip companies and public agencies across the UK, ensuring your investment delivers robust security, regulatory compliance and operational efficiency tailored to your specific requirements.
Fire Alarm Commissioning: What Gets Tested & Certified

Fire alarm commissioning is the structured test regime that verifies every device, circuit, and fault condition in your fire detection system works exactly as designed-before you accept handover and responsibility. It is not a courtesy visit or a quick demonstration; it is a documented process governed by BS 5839-1 clauses 39 and 40, producing a certificate that proves the system met acceptance criteria on a specific date. For facilities managers and responsible persons, understanding what commissioning delivers-and what it does not-is essential before signing off on a new or modified installation.

Fire Alarm Commissioning Is a Test Regime, Not a Visit

Many organisations treat commissioning as a formality: the contractor arrives, demonstrates a few devices, and hands over a certificate. In reality, fire alarm commissioning is a methodical validation of every component, zone, and operational scenario defined in the system design.

What Commissioning Actually Covers

Under BS 5839-1, commissioning includes:

  • Device activation testing: Every detector, manual call point, and input device is triggered individually to confirm correct zone indication at the panel and central monitoring station.
  • Output verification: All sounders, visual indicators, door releases, damper controls, and ancillary outputs activate on cue and meet specification.
  • Fault simulation: Power interruptions, open circuits, short circuits, and device removals are simulated to verify fault indication and system resilience.
  • Standby supply testing: Battery autonomy is measured under alarm load; recharge performance is documented.

This regime applies equally to commercial fire alarm monitoring installations and standalone systems. No device is left untested; no assumption is accepted without evidence.

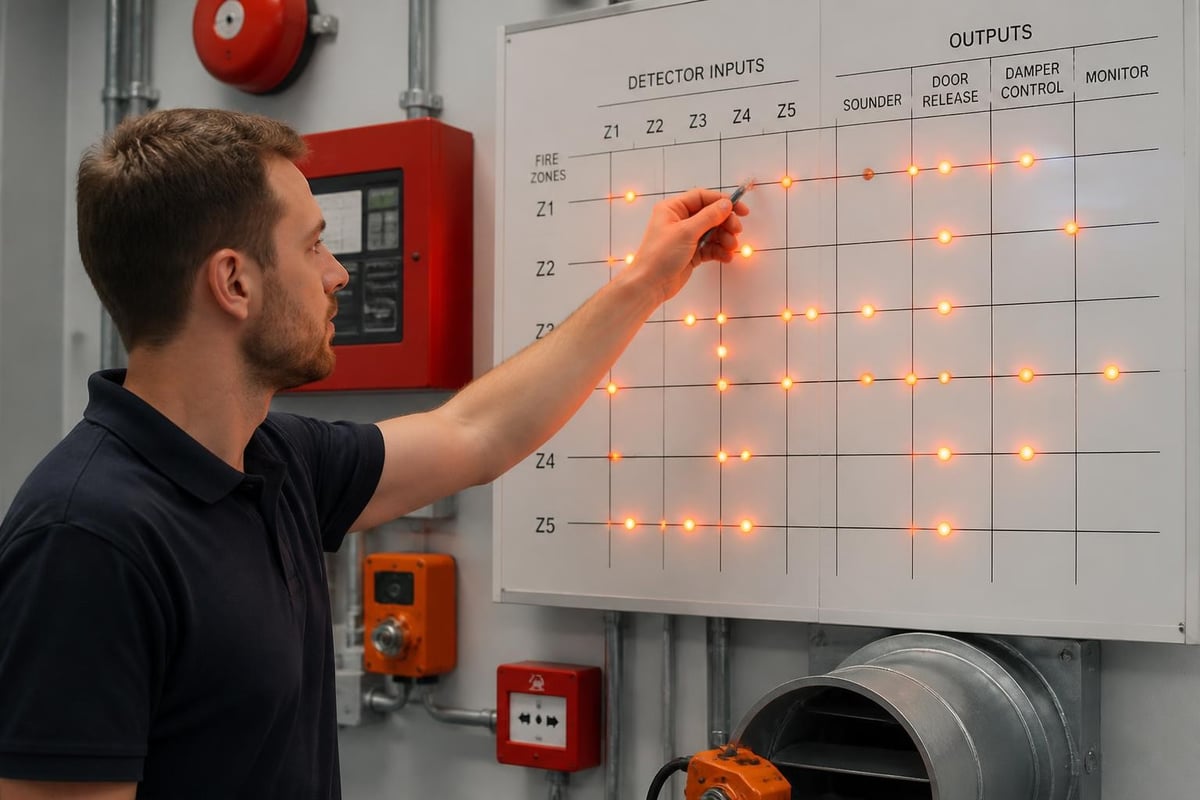
Cause and effect matrix testing

Duration and Resource Requirements

A thorough commissioning session for a medium-sized commercial building typically spans several days. Larger sites or phased handovers may require weeks of scheduled testing outside operational hours. The contractor must provide:

  • Qualified commissioning engineers (often third-party witnesses for sensitive sites)
  • Calibrated test equipment (sound meters, current measurement, battery load testers)
  • Detailed test scripts cross-referenced to the design drawings
  • Documented results for every test point

Rushing commissioning to meet an arbitrary handover date invariably leads to defects discovered during the first fire alarm servicing visit or, worse, a failed AHJ inspection.

Documents Due at Handover

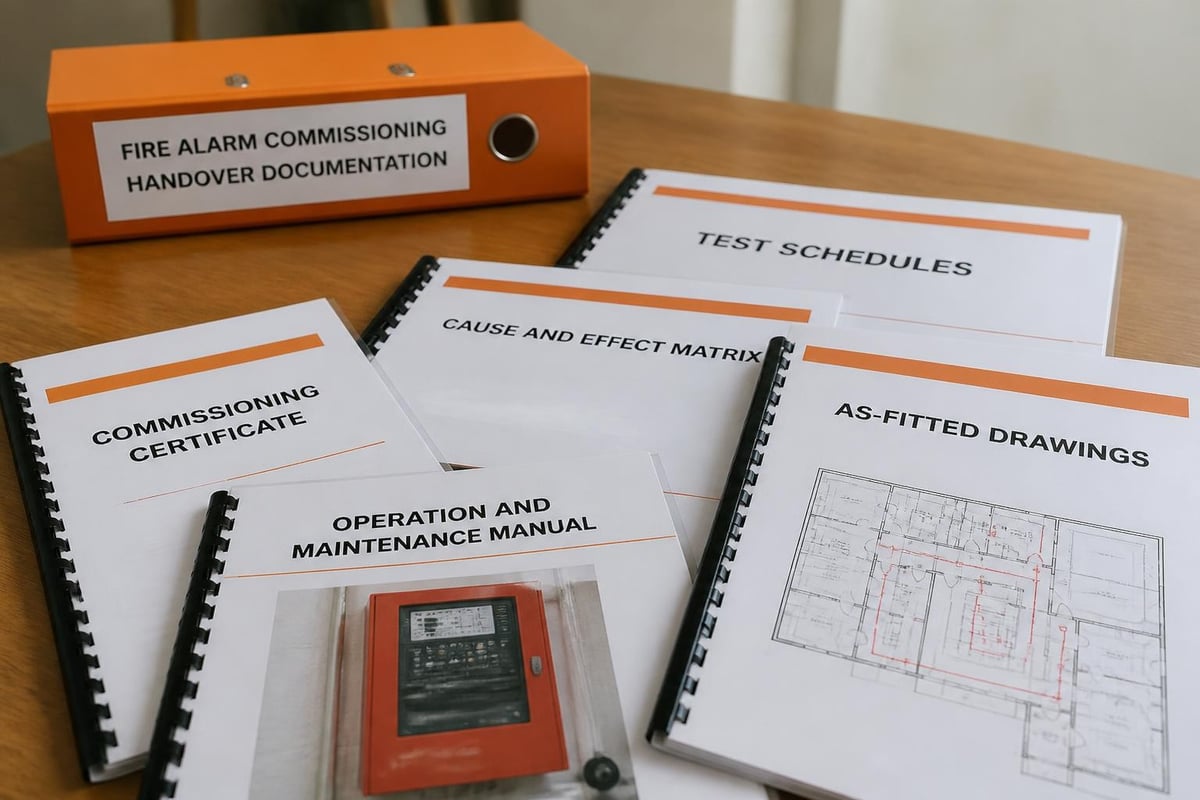
The commissioning process culminates in a handover pack. This is not a single certificate; it is a comprehensive dossier that enables you to operate, maintain, and audit the system throughout its life.

Essential Documentation

Document Purpose Retention Requirement
Commissioning certificate (BAFE SP203-1 or equivalent) Confirms acceptance tests passed; dated and signed by competent person Permanent (building file)
Test results schedule Itemises every device tested, pass/fail status, and readings (sound pressure, current draw) Permanent
Cause and effect matrix Maps each input to its intended outputs (zone logic, ancillary controls) Permanent (referenced during every service visit)
As-fitted drawings Floor plans showing final device locations, cable routes, zone boundaries Permanent (updated after alterations)
Operation and maintenance (O&M) manual System-specific procedures, manufacturer data sheets, recommended service intervals Permanent
Design compliance statement Declaration that the installation meets BS 5839-1, building regulations, and risk assessment Permanent

The Guide to the changes in BS 5839‑1:2025 introduces stricter requirements for O&M manuals, including mandatory system-specific content and clearer documentation of design deviations.

What to Check Before Accepting the Pack

  • Completeness: Do the test schedules account for every device shown on the as-fitted drawings?
  • Signatures and dates: Are all certificates signed by named individuals with stated competencies (e.g., BAFE-registered engineers)?
  • Traceability: Can you cross-reference a failed test result to a remediation entry and retest confirmation?
  • Digital formats: For larger systems, are test results provided in searchable, editable formats (not scanned PDFs of handwritten notes)?

Missing or incomplete documentation complicates future compliance audits, insurance renewals, and fault diagnosis.

Cause and Effect Testing

Cause and effect (C&E) testing validates the system's programmed logic: when detector A activates, outputs X, Y, and Z must respond within defined timescales. This is where design intent meets real-world performance.

Matrix Structure and Complexity

A C&E matrix lists every input device (detectors, call points, beam detectors, interface modules) down the left column and every output (sounders, relays, door releases, HVAC controls, monitoring signals) across the top. Each cell defines the expected response:

  • Immediate alarm: Sounders activate within 3 seconds; visual indicators flash.
  • Delayed alarm: First-stage alert for investigation areas; full evacuation after confirmation or timeout.
  • Ancillary actions: Fire doors release, dampers close, air-handling units shut down, lifts recall to ground floor.
  • No action: Detectors in non-critical zones may trigger local indication only, pending operator confirmation.

Testing involves isolating each input, activating it, and confirming every specified output operates correctly. For a 200-device system, this means 200 individual tests, each with multiple checkpoint verifications.

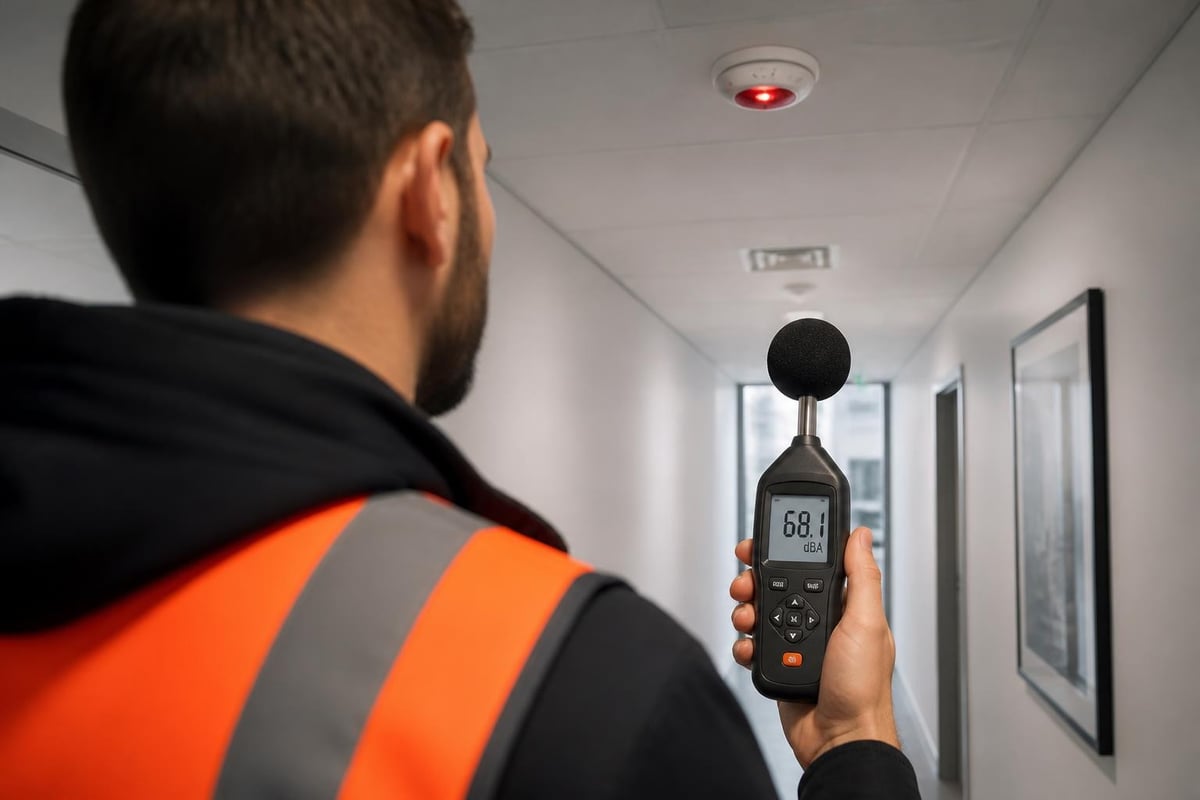
Sound pressure and audibility testing

Common Errors Found During C&E Testing

  • Cross-zone activation: Detector in Zone 3 triggers outputs assigned to Zone 5 (programming error).
  • Missing outputs: Door release or damper control specified in design but not wired or programmed.
  • Timing violations: Delayed alarms activate immediately, or immediate alarms suffer unexplained lag.
  • Monitoring signal failures: Alarm transmission to the commercial alarm monitoring centre omits critical fault or supervisory signals.

Each error must be rectified and the affected tests repeated. The final C&E matrix, signed off by the commissioning engineer, becomes the reference for all future testing and alterations.

Sound Pressure, Audibility, and Voice Intelligibility

BS 5839-1 mandates minimum sound levels to ensure occupants hear the alarm wherever they are. Commissioning must prove compliance through measurement, not assumption.

The 65dB Requirement

Fire alarm sounders must achieve 65 dB(A) at every point where people may be present, measured 1.5 metres above floor level. In areas of high ambient noise (plant rooms, workshops, kitchens), the alarm must exceed background noise by at least 5 dB(A). For sleeping accommodation, 75 dB(A) at the bedhead is required.

Commissioning engineers measure sound pressure using calibrated Class 1 sound-level meters at prescribed grid points across each room and corridor. The test schedule records:

  • Location of each measurement point
  • Background noise level (dB(A))
  • Alarm sound level (dB(A))
  • Pass/fail status against the applicable criterion

Voice Alarm Systems

For voice evacuation systems (VA), intelligibility is critical. The Common Intelligibility Scale (CIS) or Speech Transmission Index (STI) must be measured to confirm that pre-recorded or live messages are understandable above background noise and reverberation. Targets vary by building type:

  • 0.5 CIS minimum for general commercial premises
  • 0.6 CIS for large public assembly venues
  • 0.7 CIS for high-risk or complex evacuation scenarios

Testing uses acoustic test signals and specialist meters. Poor intelligibility-caused by incorrect speaker placement, inadequate power, or excessive reverberation-requires additional speakers or acoustic treatment.

What Happens If Sound Levels Fail

Failures typically arise from:

  • Insufficient sounder coverage (gaps in the design)
  • Faulty or misprogrammed sounders
  • Unexpected attenuation (heavy curtains, acoustic tiles, open-plan reconfiguration)

Remediation may involve adding devices, repositioning existing sounders, or increasing output levels. All new or relocated devices must be retested and the updated layout recorded on the as-fitted drawings.

What the Certificate Does and Does Not Certify

The commissioning certificate is a snapshot, not a perpetual guarantee. Understanding its limitations prevents false confidence.

What the Certificate Confirms

  • On the stated date, the system passed acceptance tests as witnessed by the named engineer.
  • All devices responded correctly to test stimuli.
  • Sound levels, battery autonomy, and fault responses met BS 5839-1 criteria.
  • Documentation was complete and accurate at handover.

The certificate does not confirm:

  • Ongoing reliability (systems degrade; detectors drift; batteries age).
  • Suitability for future changes in building use or layout.
  • Compliance with other standards (building regulations, insurance conditions, DSEAR, COMAH).
  • That the original design was optimal for the assessed risk.

Certification Bodies and Third-Party Validation

BAFE SP203-1 is the recognised third-party certification scheme for fire alarm installers in the UK. A BAFE-registered contractor commits to independent audits, competency verification, and standardised documentation. Certificates issued by BAFE-registered firms carry greater weight with insurers, building control, and fire authorities.

For high-risk sites (hospitals, high-rise residential, heritage buildings), specifying third-party witness testing-where an independent engineer observes and countersigns commissioning-adds an additional layer of assurance.

Aspect Self-Certified Installation BAFE-Registered Contractor Third-Party Witnessed
Design review Contractor self-assessment Independent audit of design Independent design review pre-installation
Competency verification Contractor's own records Annual BAFE audit Named CxA with documented qualifications
Documentation standards Variable BAFE SP203-1 templates Aligned with ICC G4 commissioning guidance
Insurer acceptance May require additional evidence Widely accepted Preferred for complex risks

Fire alarm commissioning documentation

Common Failures Found at First Audit

The first independent audit or service visit often reveals defects missed or glossed over during commissioning. Recognising these patterns helps you challenge incomplete handovers.

Typical Defects

  • Untested devices: Remote detectors (roof voids, riser shafts) marked "tested" without evidence.
  • Incomplete C&E validation: Matrix provided but cross-checks reveal outputs not actually verified.
  • Insufficient documentation: As-fitted drawings show original design, not post-installation changes.
  • Battery issues: Standby duration passes initial test but rapid degradation suggests poor-quality cells or incorrect charger settings.
  • Zoning errors: Floor plans mislabel zones; service engineer cannot correlate panel indications to physical locations.

Why Failures Occur

Time pressure, inadequate supervision, and cost-cutting all contribute. Commissioning is labour-intensive; shortcuts are tempting. However, the consequences-failed inspections, insurance disputes, delayed occupancy-dwarf the cost of thorough testing.

The NIST Building Fire Safety Evaluation programme has documented numerous case studies where inadequate commissioning led to detector failures in real fire scenarios, underscoring the life-safety stakes.

How to Minimise Risk

  • Specify witness testing: Require your own representative (or independent consultant) to observe random sample tests.
  • Request interim reports: For phased installations, review test schedules after each phase rather than waiting for final handover.
  • Benchmark against similar projects: If a comparable building took five days to commission, question a contractor who claims two days suffices.
  • Engage early: Involve your maintenance provider before handover; their input identifies practical concerns (access, labelling, spares) while remediation is easiest.

What to Ask Before Signing

Accepting commissioning transfers responsibility. These questions protect your interests and ensure the system is genuinely ready for operational life.

Pre-Handover Checklist

1. Has every device been individually tested?
Ask to see the test schedule. Count entries against the as-fitted drawing device count. Query any discrepancies.

2. Are all test results within specification?
Look for marginal passes (e.g., 65.2 dB(A) where 65 dB(A) is required). Confirm that values have headroom for future degradation.

3. Has the cause and effect matrix been fully validated?
Cross-reference matrix entries against actual test records. Ensure ancillary outputs (doors, dampers, HVAC) were physically observed, not just indicated on the panel.

4. Are sound pressure measurements representative?
Check that measurements include worst-case locations (furthest from sounders, high ambient noise). For phased occupancy, confirm tests occurred in representative conditions (not an empty shell).

5. Is the documentation complete and correct?
Verify serial numbers on certificates match panel labels. Ensure O&M manual is system-specific, not generic manufacturer literature.

6. What is the warranty and call-out arrangement?
Clarify response times for faults, warranty period, and transition to routine servicing. Ensure contact details and escalation procedures are documented.

7. Have building occupants been briefed?
Commissioning should include an operational demonstration for your team: how to silence alarms, reset the panel, interpret fault codes, and contact support.

Conditional Acceptance and Snagging

If defects are identified, consider conditional acceptance: sign off the majority of the system but retain a portion of the contract sum pending rectification of specific items within an agreed timeframe. Document the snagging list clearly and obtain confirmation when items are closed out.

For critical systems-particularly those linked to fire alarm installation and commissioning for high-occupancy or high-risk buildings-do not feel pressured to accept a substandard handover. The certificate you sign is evidence of your due diligence; a qualified acceptance is better than an uninformed one.

Regulatory and Insurance Implications

Authorities Having Jurisdiction (AHJ) such as local fire authorities and building control may conduct their own acceptance inspections, particularly for licensed premises, high-rise buildings, and places of assembly. Their requirements often align with BS 5839-1 but may include additional tests or documentation. For example, Fairfax County fire acceptance testing protocols specify pre-test submissions, witnessed inspections, and detailed reporting similar to UK practice.

Insurers rely on your commissioning certificate as proof of initial compliance. A certificate riddled with caveats or missing supporting documents may trigger premium loading or coverage exclusions. Conversely, comprehensive documentation from a BAFE-registered contractor strengthens your negotiating position.

Understanding Commissioning Scope for System Modifications

Fire alarm systems evolve. Extensions, panel replacements, and detector upgrades each require recommissioning-not just of new devices, but also verification that existing devices still interact correctly.

Partial vs. Full Recommissioning

  • Minor changes (individual detector replacement, like-for-like): Test the new device and verify correct zone indication. Update test records and as-fitted drawings.
  • Zone additions or cause-and-effect changes: Recommission all affected zones, retest all outputs triggered by the modified logic, and update the C&E matrix.
  • Panel replacement or system integration: Full recommissioning of the entire system. The new panel's programming may not replicate the old logic perfectly; every device and output must be revalidated.

BS 5839-1 clause 40 requires that modifications are commissioned to the same standard as new installations. Cutting corners during upgrades stores up problems: the next fire alarm servicing visit reveals inconsistencies, or worse, a real incident exposes non-functional outputs.

Documentation Updates

Every modification must be reflected in the as-fitted drawings, O&M manual, and test schedule. The date and nature of the change should be recorded, creating an audit trail that future engineers can follow. This discipline is especially critical for multi-site organisations where records management is decentralised.


Fire alarm commissioning transforms a collection of devices into a proven life-safety system. It is not a rubber-stamp exercise but a rigorous validation of design, installation quality, and operational readiness. The certificate and documentation you receive at handover enable you to operate the system confidently, demonstrate compliance to regulators and insurers, and maintain performance throughout the system's lifecycle. For comprehensive fire alarm installation and commissioning services backed by third-party certification and a commitment to thorough documentation, Logic Fire and Security supports businesses across the UK in achieving and maintaining the highest standards of fire safety compliance.

Where to Put Commercial CCTV Cameras: Placement Guide

Proper commercial cctv camera placement determines whether your video surveillance system delivers prosecution-quality evidence or merely records blurry shapes. The difference between identifying a perpetrator and watching an incident unfold without useful detail comes down to strategic positioning, appropriate mounting height, correct lens selection, and compliance with UK data protection requirements. Before specifying a single camera location, facility managers and responsible persons must define the incidents they need to evidence and work backwards to the technical parameters that deliver courtroom-standard footage.

Start From the Incident You Must Evidence, Not the Camera

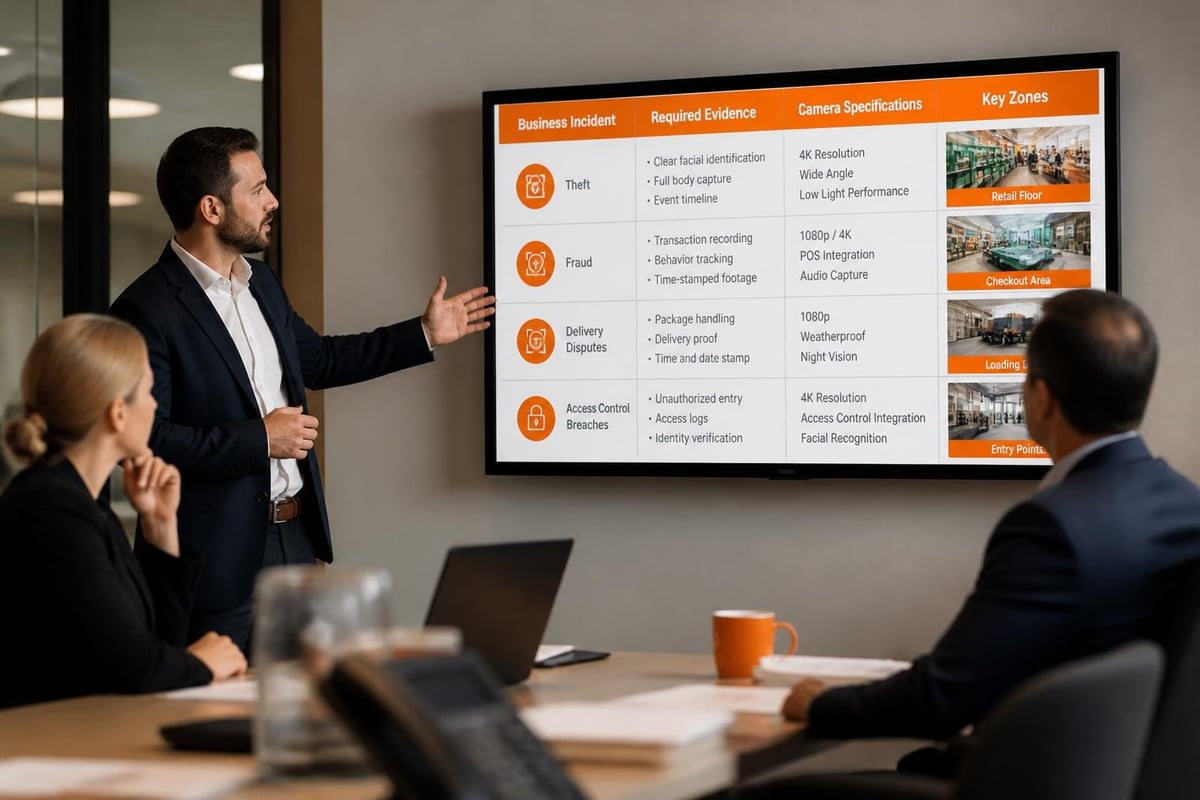
Most commercial CCTV specifications fail because they begin with camera counts and budgets rather than the business risks they must mitigate. Effective commercial cctv camera placement starts by cataloguing the incidents your organisation needs to prove or disprove: employee theft, fraudulent injury claims, shoplifting, unauthorised access, delivery disputes, or vandalism.

Each incident type demands specific image quality standards. A theft investigation requires facial identification, which the Amended Surveillance Camera Code of Practice defines as 250 pixels per metre (px/m) at the target distance. General monitoring to detect movement requires only 62.5 px/m. Observation (determining activity) needs 125 px/m.

Map Incidents to Critical Business Zones

Create a risk matrix that identifies where incidents occur, their frequency, and the evidence standard required for resolution:

Incident Type Location Required Standard Pixel Density
Till fraud Point of sale Identification 250 px/m
Stock theft Warehouse aisles Recognition (suspect known) 125 px/m
Delivery disputes Loading bay Observation (package condition) 125 px/m
Unauthorised access Fire exits Detection (movement only) 62.5 px/m

This matrix drives every placement decision. A camera positioned to "cover the warehouse" achieves nothing unless it delivers sufficient pixel density at the high-value stock locations where theft occurs. Working with experienced commercial security alarm companies ensures your system design addresses documented business risks rather than generic surveillance coverage.

Incident-driven CCTV placement strategy

Five Placements That Pay: Entrances, Till and Cash, Stock, Loading Bays, Perimeter

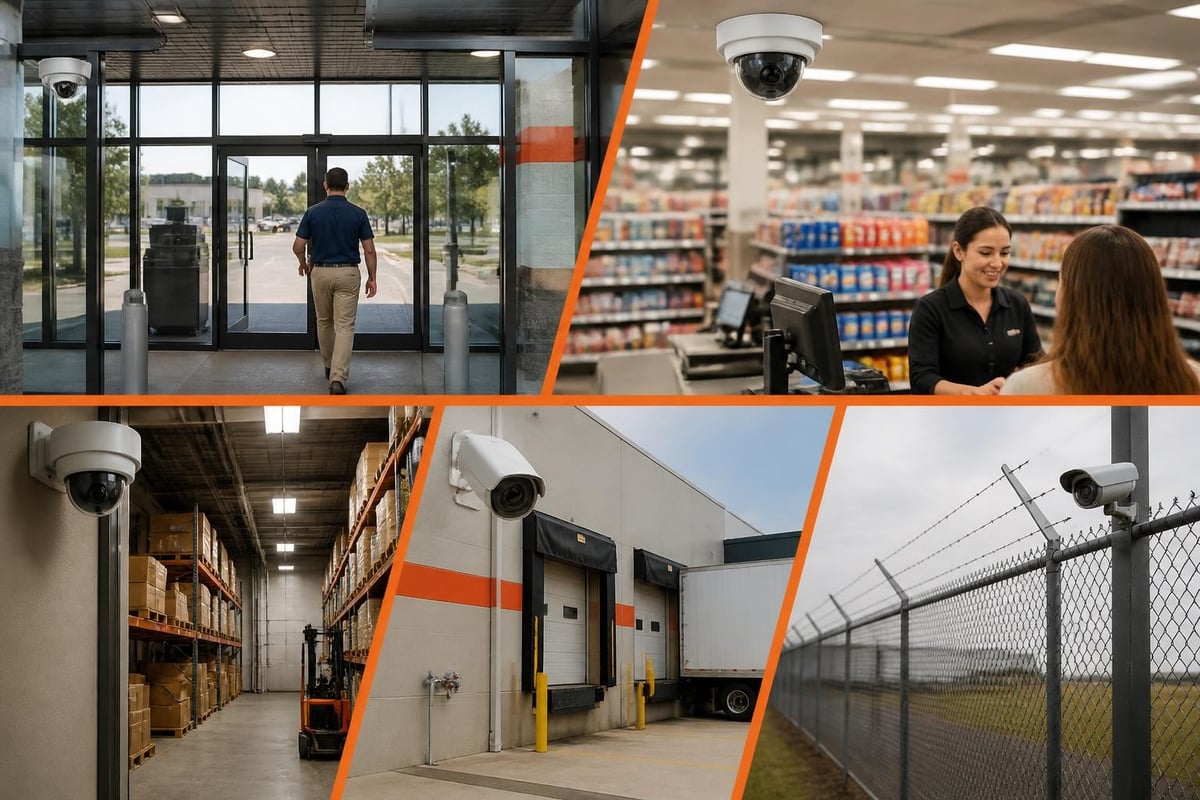
Certain zones in every commercial facility demand priority coverage because they represent the highest frequency of incidents and the greatest evidential value per camera.

Entrance and Exit Points

All personnel and visitor entry/exit points require cameras positioned to capture frontal facial images. Mount cameras above and slightly forward of the doorway, angled downward at 10-15 degrees to avoid capturing the top of heads. Target height: 2.5-3 metres for standard commercial doorways.

Place a second camera behind the threshold looking outward to capture faces of departing individuals and provide context for vehicles or accomplices. This dual-angle approach satisfies the observation standard in the DHS Video Security Systems handbook, which recommends overlapping coverage at critical chokepoints.

Reception areas benefit from three-camera coverage: wide-angle for situational awareness, medium view for face capture at the desk, and tight view for credential or document verification.

Till Points and Cash Handling Areas

Commercial cctv camera placement at point-of-sale stations must capture the till operator's actions, customer faces, and the transaction itself. Position cameras directly above the till at 2-2.5 metres, angled to include:

  • Cash drawer opening and closing
  • Card reader interactions
  • Receipt printer output
  • Operator hand movements
  • Customer face (three-quarter view minimum)

Retailers handling significant cash require a separate cash office camera covering the safe, counting table, and preparation area. Mount at ceiling height in the corner farthest from the safe to maximise coverage without blind spots behind operators.

Stock and High-Value Inventory Zones

Warehouse and stockroom coverage demands careful consideration of aisle width, ceiling height, and lighting. Standard practice positions cameras at aisle intersections, providing overlapping coverage down each corridor.

Calculate your pixel density before specifying lenses. A warehouse with 15-metre-deep aisles and 6-metre ceiling height requires varifocal lenses (typically 2.8-12mm) to deliver 125 px/m at the far end. Fixed-lens cameras lack the flexibility to adjust field of view after installation.

Critical areas include:

  • Goods-in staging areas
  • High-value product cages
  • Waste and disposal zones (common theft exit points)
  • Staff-only storage

Reference video surveillance systems for business implementation guides to understand how modern IP systems integrate inventory management data with video analytics to flag unusual access patterns.

Loading Bays and Goods Receiving

Loading bays generate frequent disputes over delivery condition, quantities, and driver behaviour. Effective commercial cctv camera placement requires:

  1. Wide-angle cameras (2.8-4mm) covering the entire bay door and approach area
  2. PTZ or varifocal cameras positioned to read vehicle registration plates and capture driver faces
  3. Detail cameras (8-12mm) focused on the handover point where goods transfer between vehicles and facility

Mount cameras under canopies or soffits where available to protect from direct weather exposure. Ensure night-time infrared coverage extends to the furthest point of the loading area, typically 20-30 metres from the building.

Perimeter and External Boundaries

External commercial cctv camera placement serves two purposes: detecting intrusion attempts and evidencing criminal damage or unauthorised access. The BSI EN IEC 62676 standard recommends overlapping coverage with no gaps exceeding 2 metres at ground level.

Position cameras at 3.5-4.5 metres to prevent tampering whilst maintaining adequate ground-level pixel density. Integrate with intruder detection systems to trigger recording and alerts when motion is detected in specified zones after hours.

Five critical commercial CCTV zones

Height, Angle, Lens: A Face at Four Metres is Useless

The physics of camera placement matter more than camera count. A £5,000 camera positioned incorrectly delivers worse results than a £500 unit placed according to optical principles.

Mounting Height and Angle

Height determines pixel density. Every metre of distance between camera and subject halves the available pixels, assuming fixed lens focal length. A camera 2 metres from a subject captures four times the facial detail of the same camera at 4 metres.

Standard commercial mounting heights by zone:

  • Corridors and aisles: 2.5-3 metres (head-height faces, minimal foreshortening)
  • Open retail floors: 3-3.5 metres (balance coverage area vs detail)
  • Warehouses: 3.5-4.5 metres (determined by racking height and aisle width)
  • External perimeter: 4-5 metres (anti-tamper height whilst maintaining ground detail)
  • Car parks: 4-6 metres (balance vehicle plate capture and pedestrian identification)

Angle affects recognition. Cameras angled more than 30 degrees from horizontal create severe foreshortening that distorts faces and makes identification unreliable. The Washington State facility design guidelines specify maximum 20-degree downward angle for facial identification purposes.

Lens Selection and Field of View

Three lens categories serve distinct commercial applications:

Lens Type Focal Length Use Case Coverage at 3m Height
Wide angle 2.8-4mm General awareness, small rooms 8-12 metre width
Standard 6-8mm Corridors, medium rooms, till points 4-6 metre width
Telephoto 12mm+ Long corridors, vehicle plates, perimeter 2-3 metre width

Varifocal lenses (adjustable focal length) cost 30-40% more than fixed lenses but eliminate the risk of incorrect field-of-view specifications during installation. For projects requiring more than ten cameras, varifocal units significantly reduce commissioning time and rework costs.

Calculate before you buy. Online field-of-view calculators (available from major manufacturers) require three inputs: sensor size, lens focal length, and distance to subject. These tools reveal whether your specification achieves the required pixel density before equipment purchase.

UK Winter Low Light and Weather Considerations

British weather conditions expose poor commercial cctv camera placement decisions. Systems that perform adequately in summer daylight fail completely during winter months unless specified correctly from the outset.

Low-Light Performance

December through February presents challenging conditions: extended darkness, heavy cloud cover, and reliance on artificial lighting. Cameras require minimum illumination ratings below 0.01 lux for acceptable performance in car parks, perimeters, and loading areas during early morning hours.

Infrared (IR) illumination extends usable range in complete darkness but introduces three complications:

  1. IR reflection from glass, shiny surfaces, and rain creates unusable glare
  2. IR absorption by dark clothing and vehicles reduces effective range
  3. Insect attraction to IR emitters creates motion-detection false alarms

Position IR cameras to avoid pointing directly at windows, wet surfaces, or highly reflective signage. Where IR proves impractical, consider white-light illuminators that provide colour images at night and serve as visual deterrents.

Environmental Protection Standards

External cameras require IP66 or IP67 ratings (dust-tight, protected against heavy seas or powerful jets). Internal cameras in dusty warehouses or food preparation areas need minimum IP54 (limited dust ingress protection).

Condensation kills more cameras than physical damage. Cameras experiencing temperature cycling (cold nights, warm days) or installed in high-humidity environments require integrated heaters and IP67-rated cable glands. Budget £30-60 per camera for environmental housings on external installations.

Coastal locations and areas with high atmospheric salt content (within 10 miles of the coast across much of the UK) demand stainless steel or corrosion-resistant housings for external cameras. Standard powder-coated aluminium housings corrode within 3-5 years in marine environments.

Pixel Density Decides Identify or Just Show

The single most important technical specification for commercial cctv camera placement is pixel density at the point of interest. Every other parameter (camera count, recording duration, storage capacity) derives from this fundamental requirement.

Calculating Required Megapixels

Pixel density (px/m) depends on three variables:

  • Sensor resolution (total megapixels)
  • Lens focal length
  • Distance to subject

Worked example: A 2-megapixel camera (1920 × 1080 pixels) with 4mm lens positioned 5 metres from a doorway delivers approximately 90 px/m. This meets the observation standard (125 px/m) but fails identification requirements (250 px/m).

To achieve identification standard at 5 metres, the same installation requires either:

  • A 5-megapixel sensor (2560 × 1920 pixels) with 4mm lens, or
  • A 2-megapixel sensor with 8mm lens (narrower field of view)

Recent research on optimal camera placement algorithms demonstrates that strategic positioning reduces required camera counts by 40-60% compared to conventional uniform coverage approaches whilst improving evidential quality.

Multi-Imager and Panoramic Solutions

Single high-resolution panoramic cameras (12-20 megapixels) or multi-imager units (four sensors in one housing) offer alternatives to multiple individual cameras in open areas. These units provide 180-360 degree coverage with digital zoom capability for incident investigation.

Advantages: Reduced installation labour, fewer network switch ports, simplified cabling.

Limitations: Higher per-unit cost (£800-2,500), greater bandwidth requirements, single point of failure covers large area.

Panoramic cameras suit reception areas, retail floors, and car parks where situational awareness matters more than identification-quality close-ups.

Pixel density and evidence standards

Privacy Masking and Signage First

Legal compliance governs commercial cctv camera placement as much as technical capability. UK organisations operating surveillance systems face obligations under GDPR, Data Protection Act 2018, and sector-specific regulations.

Privacy Impact Assessment

Before deploying cameras, the responsible person must complete a Privacy Impact Assessment (PIA) documenting:

  • Legitimate business purposes for surveillance
  • Proportionality (least intrusive means of achieving objectives)
  • Privacy risks to employees, visitors, and neighbouring properties
  • Mitigation measures including privacy masking

Camera views must exclude areas where individuals have reasonable expectation of privacy: toilets, changing rooms, medical facilities, private offices (unless consent obtained), and neighbouring properties. Modern IP cameras include software privacy masking that blacks out specified zones whilst recording the remainder of the field of view.

The ICO CCTV Code of Practice requires organisations to demonstrate that surveillance is necessary, proportionate, and cannot be achieved through less intrusive means.

Signage and Notification Requirements

Prominent signage must appear at all entrances to surveilled areas, stating:

  • That CCTV is in operation
  • The identity of the data controller (your organisation)
  • Contact details for data protection enquiries
  • The legal basis for processing (legitimate interests, typically)

Signs should appear before individuals enter the camera coverage area, giving opportunity to avoid the surveilled zone if desired. The Epping Forest CCTV Code of Practice provides exemplar signage templates applicable to commercial installations.

Data Retention and Access Controls

Commercial installations typically retain footage for 30 days unless specific incidents require extended preservation. Longer retention periods increase storage costs and heighten data protection risks without corresponding security benefits.

Access controls must restrict footage viewing to authorised personnel only. Modern systems integrate with security and access control platforms to audit who viewed footage, when, and for what purpose. This audit trail proves essential when responding to subject access requests or defending employment tribunal claims.

Network Security for IP Camera Systems

IP-based surveillance systems require the same cybersecurity rigour as other networked devices. The NIST Guide to Operational Technology Security recommends segregating camera networks from corporate IT infrastructure using VLANs or physically separate switches.

Minimum security measures include:

  • Changing default passwords on all cameras and NVRs
  • Disabling unused network services (UPnP, Telnet)
  • Implementing certificate-based encryption for video streams
  • Regular firmware updates from manufacturers
  • Network intrusion detection monitoring camera network segments

Compromised camera systems provide attackers with visual reconnaissance of facilities and potential pivot points into broader networks. Organisations with remote CCTV monitoring services must ensure third-party monitoring centres maintain equivalent security standards.

System Integration and Ongoing Verification

Effective commercial cctv camera placement delivers sustained value only when integrated with broader security infrastructure and regularly verified against original specifications.

Integration With Access Control and Alarms

Camera systems should trigger recording when integrated systems detect events:

  • Door controllers initiate recording when specific doors open outside normal hours
  • Intruder alarms direct cameras to affected zones and increase frame rates
  • Fire alarm systems capture evacuation footage and preserve evidence of fire origin

This event-driven approach reduces storage requirements whilst ensuring high-quality footage captures significant incidents. Integration also enables guard tour verification, where warehouse security alarm systems confirm that patrols occurred at specified times by cross-referencing alarm acknowledgements with camera footage.

Video Analytics and Intelligent Monitoring

Modern IP cameras include analytics capabilities that automate incident detection:

  • Line crossing: Triggers when individuals cross virtual boundaries (perimeter fences, restricted areas)
  • Loitering detection: Alerts when persons remain in defined zones beyond set durations
  • Object removal: Flags when items disappear from protected areas
  • Crowd density: Monitors occupancy levels in public areas

Analytics reduce dependence on continuous human monitoring but require careful configuration to minimise false alarms. Accuracy improves with strategic camera placement: analytics perform best with clear, unobstructed views and consistent lighting.

Quarterly Performance Verification

Camera systems degrade over time through:

  • Lens contamination (dust, moisture, insect debris)
  • Bracket creep (mounting hardware loosening)
  • Vegetation growth obscuring fields of view
  • Lighting changes (failed lamps, seasonal shadows)

Quarterly inspections should verify each camera against original field-of-view diagrams, check recording quality, and test night-time performance. Many organisations discover failed cameras only when footage is required to investigate incidents weeks after the failure occurred.

Maintenance contracts with qualified providers ensure systematic verification and rapid fault response. Systems protecting critical infrastructure or high-value assets justify monthly verification schedules.


Strategic commercial cctv camera placement transforms surveillance from a recording exercise into an evidential asset that supports prosecution, resolves disputes, and demonstrates duty-of-care compliance. Successful implementations prioritise incident-driven specifications, evidence-quality pixel density, UK weather resilience, and data protection compliance from the initial design stage. Logic Fire and Security brings over two decades of experience designing, installing, and maintaining commercial surveillance systems for Blue Chip companies and public agencies across the UK, ensuring your cameras deliver prosecution-standard evidence when it matters most.

Our Accreditations

Work
For Us